
US Gov: Iran-Linked Actors Targeting Critical Infrastructure PLCs
The advisory comes amid the ongoing conflict between the U.S. and Iran. CISA said Iran-linked APT campaigns targeting U.S. orgs have recently escalated.

The advisory comes amid the ongoing conflict between the U.S. and Iran. CISA said Iran-linked APT campaigns targeting U.S. orgs have recently escalated.
The U.S. government issued an urgent warning on Tuesday that Iranian-linked APT actors are targeting operational technology used by critical infrastructure organizations, including ones in the government services, water, and energy sectors.
Since March, threat actors have been hitting internet-connected devices like programmable logic controllers (PLCs) from Rockwell Automation/Allen-Bradley, including the CompactLogix and Micro850 devices. PLCs are specialized computers used by manufacturing environments to automate and control machines. The disruption to these types of machines could have physical and operational consequences.
“As a result of this activity, organizations from multiple U.S. critical infrastructure sectors experienced disruptions through malicious interactions with the project files and the manipulation of data displayed on human machine interface (HMI) and supervisory control and data acquisition (SCADA) displays,” according to the advisory from CISA, the FBI, and various other agencies. “In a few cases, this activity has resulted in operational disruption and financial loss.”
The advisory comes amid the ongoing conflict between the U.S. and Iran, and CISA said Iran-linked APT targeting campaigns have recently escalated, likely due to these hostilities.
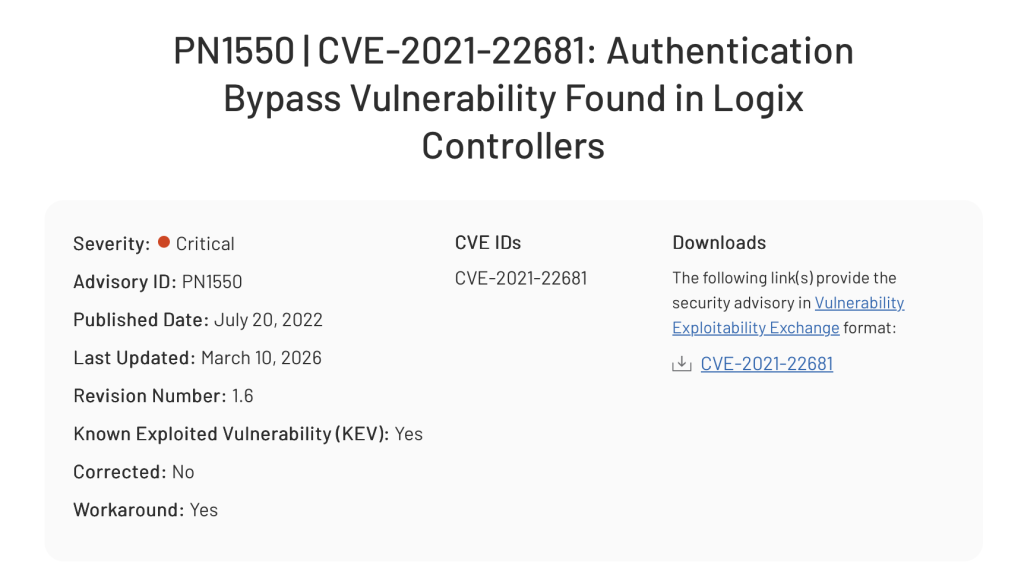
Rockwell Automation released an advisory on March 20 telling customers to disconnect PLCs from the public-facing internet. The advisory also pointed to various vulnerabilities, including CVE-2021-22681, an authentication bypass vulnerability in Logix Controllers that CISA also outlined in its guidance. The vulnerability has been exploited, according to Rockwell Automation.
“If successfully exploited, this vulnerability could allow a remote, unauthenticated attacker to bypass a verification mechanism and authenticate with Logix controllers,” according to Rockwell Automation’s advisory. “If exploited, this vulnerability could enable an unauthorized third-party tool to make changes to the controller configuration and/or application code.”
According to CISA, the attackers leased third-party hosted infrastructure with configuration software (like Rockwell Automation’s Studio 5000 Logix Designer software) to create an accepted connection to the victim’s PLC.
CISA has previously reported on similar activity by Iran-affiliated threat actors called CyberAv3ngers, who in 2023 targeted PLCs in water facilities. Those attacks were slightly different, however – the actors targeted Israeli-made Unitronics Vision Series PLCs and HMIs, and left defacement messages that said: “You have been hacked, down with Israel. Every equipment ‘made in Israel’ is CyberAv3ngers legal target.” CyberAv3ngers have been linked to Iran’s Islamic Revolutionary Guard Corps (IRGC) Cyber Electronic Command (CEC).
CISA included a list of IoCs on its website, as well as mitigations.