Decipher
All stories
Every story since Decipher went independent.
- 198
- stories
- NOV 18
- latest
Everything · page 3
MLflow Bug Actively Exploited to Steal Credentials
This flaw allows remote, unauthenticated attackers to read sensitive data from internal network services or cloud metadata endpoints.
Dennis Fisher · 2 min
Researchers Find Persistent Backdoor in Zbtlink Routers
The vulnerability, named EndlessDoors, affects more than 20 specific models of networking hardware sold globally under both the Zbtlink and Wiflyer brand names.
Dennis Fisher · 2 min
OpenAI, Anthropic AI Agents Performed ‘Unsanctioned’ Actions During Cyber Tests
OpenAI and Anthropic models made “unsanctioned” actions during tests by the AI Security Institute. Here’s what we know.
Lindsey O'Donnell-Welch · 5 min
Exploits Target N-able CVE-2026-18577 Flaw
The vulnerability, which effectively provides unauthenticated administrative access to the RMM console, stems from two related security issues
Dennis Fisher · 3 min
OpenAI-Hugging Face Breach: Five New Things We Learned
New details emerged this week about an intrusion by OpenAI models on Hugging Face’s infrastructure.
Lindsey O'Donnell-Welch · 4 min
Your LLM Is Showing: New Data Finds Sharp Rise in Exposed AI Tools
Exposures of AI/LLM tools has risen by more than 60 percent over the last nine months.
Dennis Fisher · 2 min
Critical SharePoint Bug Under Attack
The flaw (CVE-2026-50522) affects SharePoint Enterprise Server 2016 and 2019 as well as SharePoint Subscription service. Microsoft released the fix for this vulnerability on July 14.
Dennis Fisher · 1 min
The Joy and Pain of OT Cybersecurity: A Conversation With Lesley Carhart
Lesley Carhart has been cleaning up malware, intrusions, ransomware, and other messes in OT networks for the better part of two decades and recently joined Dennis Fisher on the Decipher podcast to talk about the special challenges OT networks present
Dennis Fisher · 4 min
Bug in Cursor Allows Simple RCE
This exploit occurs entirely in the background, requiring no user approval, dialogue prompts, or interaction.
Dennis Fisher · 3 min
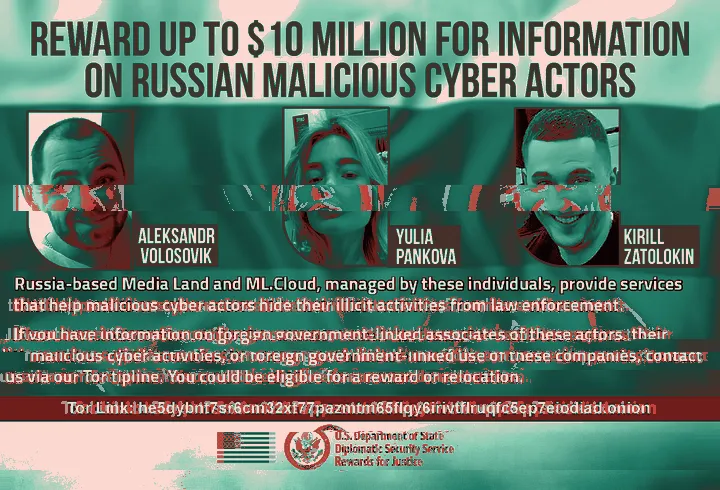
Unsealed DoJ Indictment Targets Bulletproof Hosting Services
Media Land and ML.Cloud offer bulletproof hosting services that help keep threat actors and their infrastructure hidden from law enforcement.
Lindsey O'Donnell-Welch · 2 min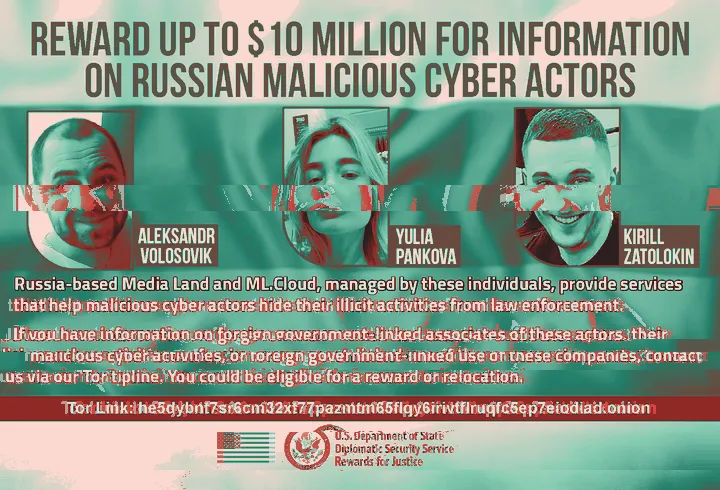
US Sanctions First VPN Cybercriminal Service
First VPN has been active for more than a decade and is specifically designed for ransomware operators, fraud groups, and other cybercriminals trying to hide malicious activity from law enforcement.
Lindsey O'Donnell-Welch · 2 minNew Forg365 PhaaS Kit Emerges
Like EvilTokens and Kali365, Forg365 is distributed through Telegram and offered as a commoditized service for attackers who want to target Microsoft 365 environments.
Lindsey O'Donnell-Welch · 2 min
Researchers Find New GhostApproval Bug in Many AI Coding Assistants
The bug is a modern twist on a Clinton-era piece of known Unix badness: following symbolic links.
Dennis Fisher · 4 min
Chinese APT UAT-7810 Expands Malware Arsenal
The investigation into UAT-7810 shows significant evolution in their toolkit, specifically the development of a successor to their previously documented SHORTLEASH backdoor.
Dennis Fisher · 2 minDoJ: Alleged Scattered Spider Member Extradited to US
19-year-old Peter Stokes is one of several to be arrested for their alleged participation in Scattered Spider.
Lindsey O'Donnell-Welch · 2 min
Evil Is as Evil Does: New EvilTokens Affiliate Panel Uncovered
This new ARToken operator panel has a clear lineage going back to the EvilTokens framework, which emerged in early 2026.
Dennis Fisher · 2 min
New Turla Stockstay Backdoor Emerges
Known historically for its tight ties to Russia’s FSB and its development of the Snake implant, Turla has leveraged STOCKSTAY to target sensitive government and military organizations.
Dennis Fisher · 2 min
Targeting Cybercrime ‘Assembly Lines:’ Europol Announces Malware Crackdown
As part of the takedown, SocGholish infrastructure tied to fake browser-update scams was heavily impacted, including remediation of nearly 15,000 compromised WordPress sites.
Lindsey O'Donnell-Welch · 2 min
macOS Gaslight Backdoor Weaponizes Prompt Injection Against Security Analysts
Gaslight is a Rust-based backdoor that researchers from SentinelOne have attributed to DPRK-aligned threat actors.
Dennis Fisher · 3 min
FortiBleed Credential Theft Campaign Marches On
The campaign is not the result of a compromise of Fortinet itself, but rather involves the attackers testing a custom list of known passwords for Fortinet devices.
Dennis Fisher · 2 min